

Share Post


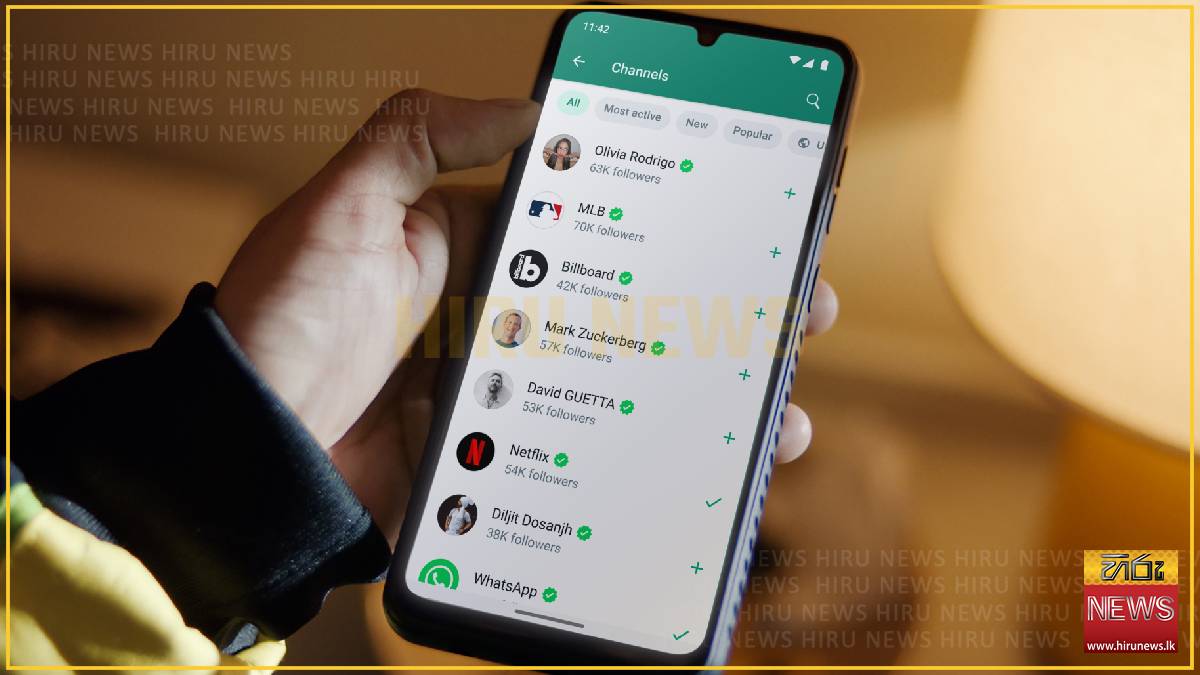
A newly emerged zero-click cyberattack targeting WhatsApp users raised concerns among iPhone users in Sri Lanka, with several individuals reportedly complaining to the Sri Lanka Computer Emergency Readiness Team (Sri Lanka CERT) after their accounts were compromised.
The attack is believed to target vulnerable iPhones running older versions of iOS and can allow attackers to take control of WhatsApp accounts without requiring victims to click a malicious link, scan a QR code, or otherwise interact with the attack.
Several members of the media and business community in Sri Lanka reportedly experienced or reported incidents linked to the attack, indicating that the threat is not limited to overseas users.
According to a forensic investigation by an Italian cybersecurity firm, the attackers may exploit vulnerabilities associated with the synchronisation of linked devices.
In reported cases, compromised accounts were used to send unauthorised WhatsApp messages requesting money transfers. In some instances, victims reportedly found no suspicious devices listed under the linked-device settings of WhatsApp, making the takeover more difficult to detect.
Attackers also allegedly took control of WhatsApp group administrator privileges after compromising accounts.
The attack is reportedly associated with iPhones running versions earlier than iOS 16.7.12, highlighting the risks posed by outdated operating systems.
Unlike conventional WhatsApp scams involving QR-code phishing or malicious links, the reported zero-click technique does not require direct interaction from the victim, making it particularly difficult for users to identify and prevent.
Cybersecurity experts advise WhatsApp users to immediately update their iPhones to the latest supported iOS version and install the latest WhatsApp update.
Users are also encouraged to enable the two-step verification and Chat Lock features of WhatsApp. They further advised users to independently verify unusual requests for money or sensitive information through another trusted communication channel, even when such requests appear to come from a known contact.
The incident highlights growing concerns over the use of sophisticated zero-click exploitation techniques by financially motivated cybercriminals and underscores the importance of keeping mobile operating systems and applications updated.
The attack is believed to target vulnerable iPhones running older versions of iOS and can allow attackers to take control of WhatsApp accounts without requiring victims to click a malicious link, scan a QR code, or otherwise interact with the attack.
Several members of the media and business community in Sri Lanka reportedly experienced or reported incidents linked to the attack, indicating that the threat is not limited to overseas users.
According to a forensic investigation by an Italian cybersecurity firm, the attackers may exploit vulnerabilities associated with the synchronisation of linked devices.
In reported cases, compromised accounts were used to send unauthorised WhatsApp messages requesting money transfers. In some instances, victims reportedly found no suspicious devices listed under the linked-device settings of WhatsApp, making the takeover more difficult to detect.
Attackers also allegedly took control of WhatsApp group administrator privileges after compromising accounts.
The attack is reportedly associated with iPhones running versions earlier than iOS 16.7.12, highlighting the risks posed by outdated operating systems.
Unlike conventional WhatsApp scams involving QR-code phishing or malicious links, the reported zero-click technique does not require direct interaction from the victim, making it particularly difficult for users to identify and prevent.
Cybersecurity experts advise WhatsApp users to immediately update their iPhones to the latest supported iOS version and install the latest WhatsApp update.
Users are also encouraged to enable the two-step verification and Chat Lock features of WhatsApp. They further advised users to independently verify unusual requests for money or sensitive information through another trusted communication channel, even when such requests appear to come from a known contact.
The incident highlights growing concerns over the use of sophisticated zero-click exploitation techniques by financially motivated cybercriminals and underscores the importance of keeping mobile operating systems and applications updated.
Latest News
AI model Claude discovers CRISPR-like enzyme system, Anthropic says
Local
24 September 2026

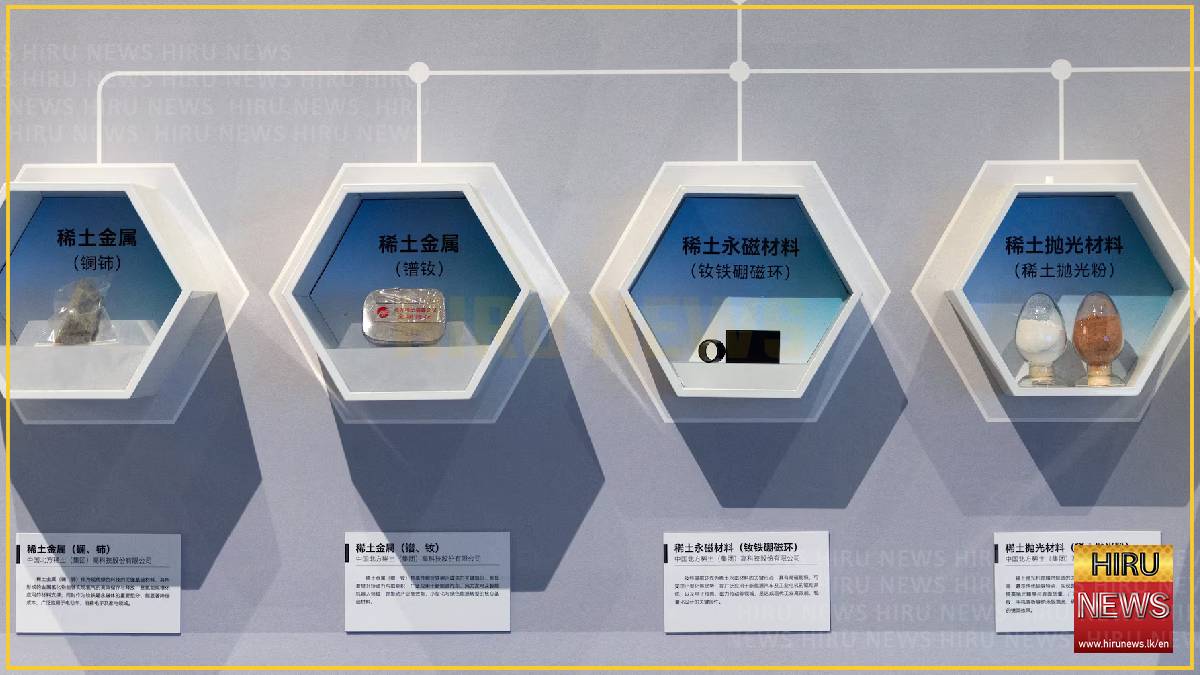
China's rare earths dominance to overshadow Trump's talks with Xi
Local
24 September 2026
OpenAI, Anthropic CEOs call for global AI regulation at UN
Local
24 September 2026
Turkiye agrees to gradual handover of Bashiqa base to Iraq
Local
24 September 2026
SLIC General appoints Asiri Wickramarachchi as Acting CEO
Local
24 September 2026
Dick Guttman, renowned Hollywood publicist to stars dies at 93
Local
24 September 2026

Norway gives additional $13 million in aid to Palestinians
Local
24 September 2026
China's high-speed race for fast-charging EVs
Local
24 September 2026

Auto Direct introduces Lanka’s first Nissan Tekton
Local
24 September 2026

Flash Health expands Cashless OPD with McLarens Group
Local
24 September 2026